About the website
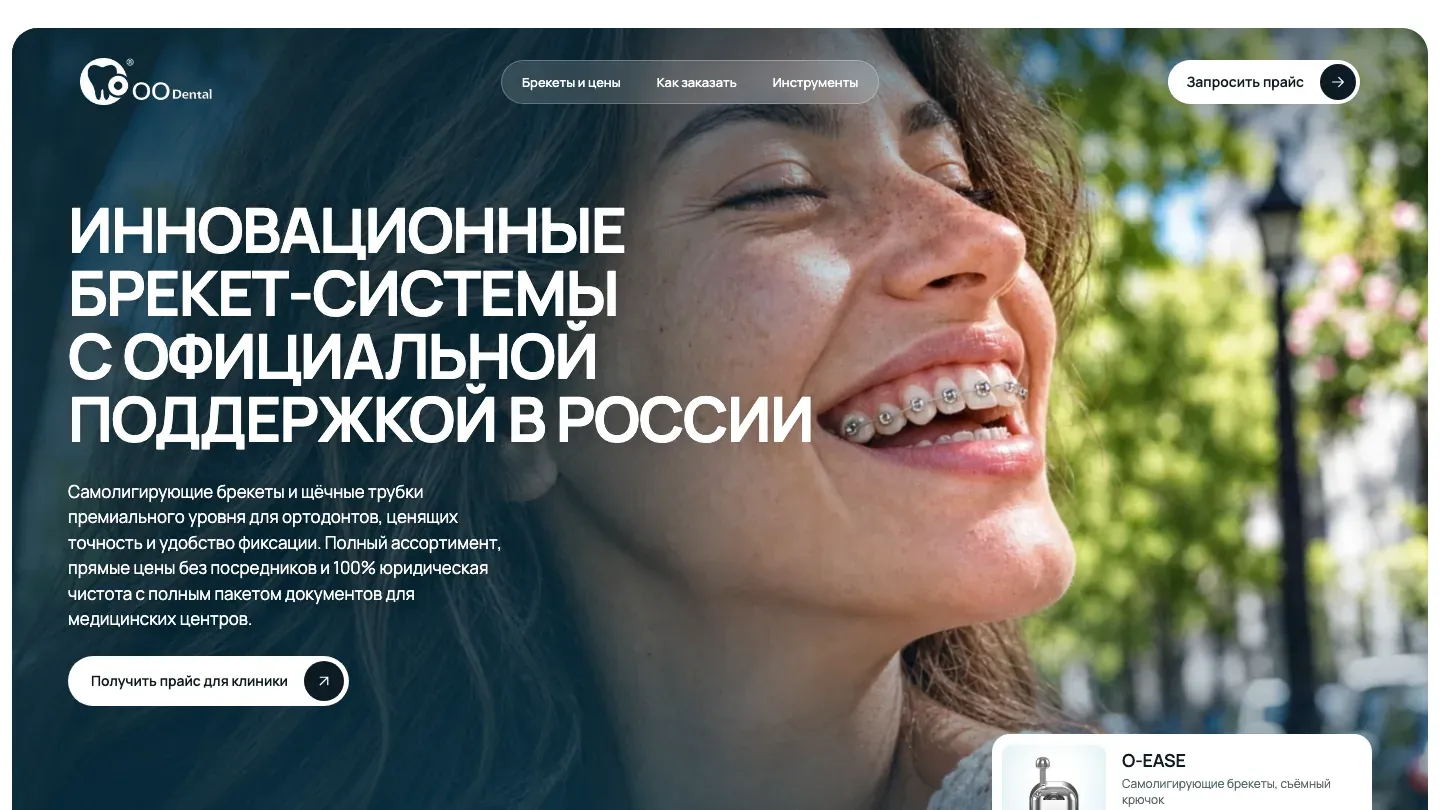
OO Dental product ranges for orthodontists and purchasing teams. Each product has specifications and price options; catalogues are available to download, and a separate page explains how to order.
What I did
- Savings against the retail price are shown next to each price, so the benefit of buying a larger volume is clear.
- Clicking the right price carries the chosen purchase terms into the next step of the order.
- A quiz starts with simple questions about the purpose and volume of the purchase, even if the customer has not chosen a product yet.
- The button for requesting registration documents fills in the right enquiry text by itself.
- A 3D jaw model with every type of bracket system, to see straight away how it will look on a patient.
- Instrument search by name, model, article number and description. Found items can be put straight into one request with the quantities needed.
Website CMS
- Price logic checks: the system will not save a wholesale price higher than the clinic or retail price.
- Linked price updates: changes are applied to product cards, tables and structured data; savings against the retail price are recalculated automatically.
- An editor for the long list of instruments: search by model and article number speeds up work on specific items.
- Drafts kept apart from publishing: changes can be checked on the pages before visitors see them.
- Rolling back to an earlier version: the last 20 published versions are kept and can be restored.
- Panel protection: limited login attempts, secure sessions, verification of edit commands and protection against overwriting edits made in another tab.
Security
Before handing the project over to the client, an internal grey-box security audit was carried out.
Result: No critical, high or medium vulnerabilities were found in the final build of the project.
Protection against SQL and command injection
- Test: Automated parameter testing with
sqlmapplus manual fuzzing of input forms. - How it is protected: The source code never builds SQL queries by joining strings. The framework’s built-in ORM escaping is used. The application’s database access is limited to
Data Reader/Writerrights, with no access to system tables.
Protection against XSS
- Test: Attempts to inject malicious JS scripts into every user text field.
- How it is protected: A strict template engine with automatic escaping of HTML entities. A strict Content Security Policy (CSP) on the web server blocks any third-party or unsafe inline code.
Component security
- Test: Software composition analysis (SCA) with
SnykandDependency-Check. - How it is protected: All packages are pinned to stable versions with no known vulnerabilities in the NVD database. Automatic notifications are set up for security patches to dependencies.
Admin panel isolation
- How it is protected: The admin panel is moved to a separate subdomain, hidden from search engine crawlers and protected from brute force by
Fail2ban(the IP is blocked after 5 failed attempts). Signing in to the admin panel requires two-factor authentication (2FA / TOTP).
Resilience to DDoS and load
- Test: Stress testing with
k6, simulating a legitimate surge of users and HTTP flood attacks. - How it is protected: Request limits (
limit_req) are set in Nginx and return error 429 when one IP exceeds them. The architecture is ready for seamless integration with external services (for example, Cloudflare / Qrator) to filter L4/L7 traffic.