About the website
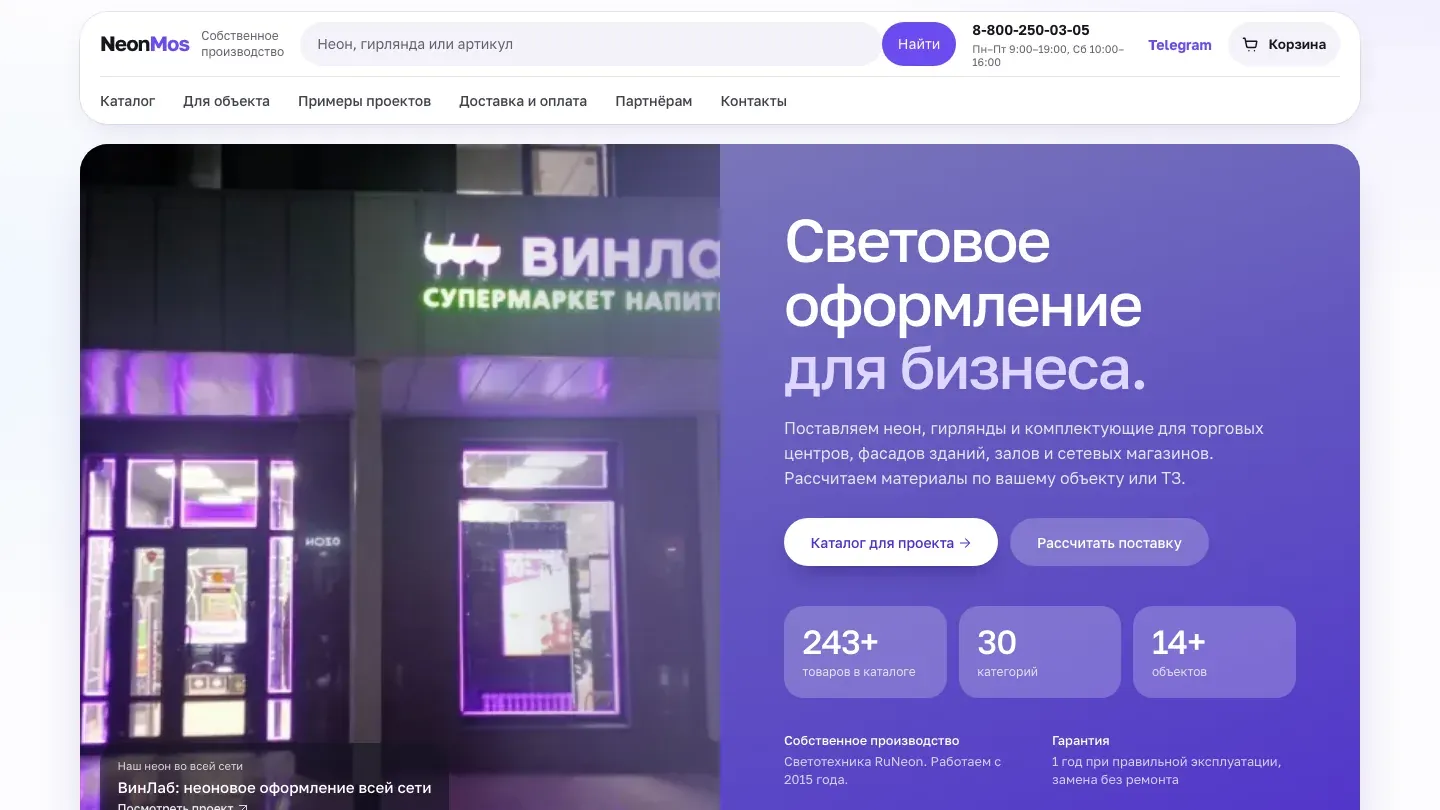
Neon, string lights and other lighting products next to photos of commercial installations. Customers can put together a lighting specification for a building or a retail chain and send it as a project request.
What I did
- Lighting is chosen by task, colour and length, with no need to know the technical names.
- Neon accessories are calculated automatically, so the customer does not have to put together a compatible set themselves.
- A product can be added together with its accessories in one click.
- The cart is saved between visits.
- Products and project details are passed into the enquiry automatically.
- Extra form fields are tucked under an expandable block, so the customer is not overloaded at first.
- Search understands typos, the wrong keyboard layout and transliteration, and searches by specifications. For example, «неон», “neon” and “ytjy” all lead to the right product; different ways of writing sizes and voltage are brought to one form.
Website CMS
- Built-in enquiry analytics: a “visit → form start → submission” funnel, sources and UTM ad campaigns.
- Product interest report: shows which products, categories and ready-made solutions visitors look at.
- Enquiries arrive with the order already filled in: products, quantities, attached files and the page the enquiry came from are in the manager’s card.
- Enquiries are split by task: product purchase, project calculation, dealer request, callback or question.
- One search across the admin panel: products, article numbers, categories, articles, installations and page fields are found from one place.
- All commercial content is managed in one place: range, prices, installations, articles, SEO and redirects.
- Verified backups: the database, images and enquiry files are packed into an archive with a database integrity check and a checksum.
- Protected access: passwords are stored as strong hashes, and admin sessions expire after a limited time.
Security
Before handing the project over to the client, an internal grey-box security audit was carried out.
Result: No critical, high or medium vulnerabilities were found in the final build of the project.
Protection against SQL and command injection
- Test: Automated parameter testing with
sqlmapplus manual fuzzing of input forms. - How it is protected: The source code never builds SQL queries by joining strings. The framework’s built-in ORM escaping is used. The application’s database access is limited to
Data Reader/Writerrights, with no access to system tables.
Protection against XSS
- Test: Attempts to inject malicious JS scripts into every user text field.
- How it is protected: A strict template engine with automatic escaping of HTML entities. A strict Content Security Policy (CSP) on the web server blocks any third-party or unsafe inline code.
Component security
- Test: Software composition analysis (SCA) with
SnykandDependency-Check. - How it is protected: All packages are pinned to stable versions with no known vulnerabilities in the NVD database. Automatic notifications are set up for security patches to dependencies.
Admin panel isolation
- How it is protected: The admin panel is moved to a separate subdomain, hidden from search engine crawlers and protected from brute force by
Fail2ban(the IP is blocked after 5 failed attempts). Signing in to the admin panel requires two-factor authentication (2FA / TOTP).
Resilience to DDoS and load
- Test: Stress testing with
k6, simulating a legitimate surge of users and HTTP flood attacks. - How it is protected: Request limits (
limit_req) are set in Nginx and return error 429 when one IP exceeds them. The architecture is ready for seamless integration with external services (for example, Cloudflare / Qrator) to filter L4/L7 traffic.