About the website
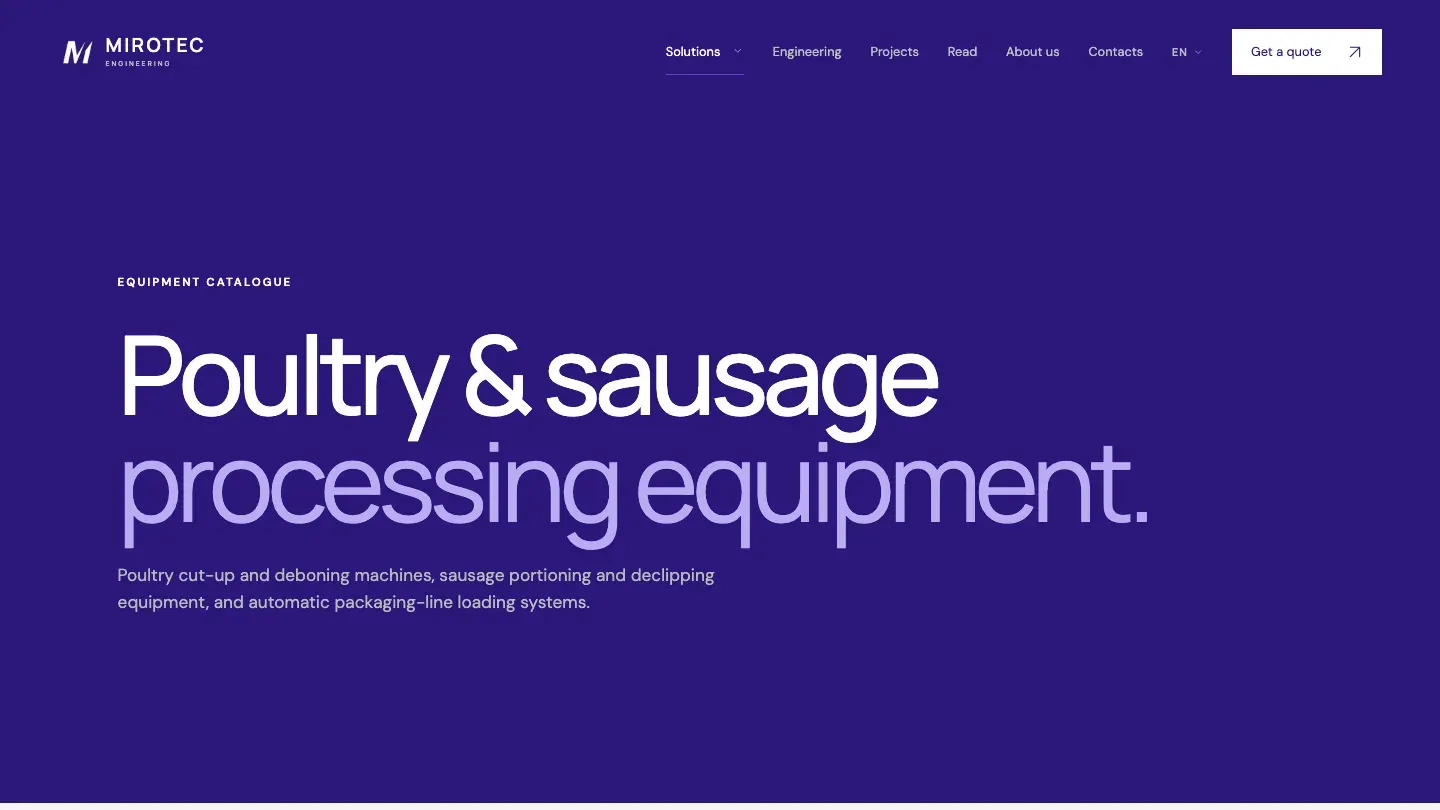
The English-language site for international buyers of poultry processing and sausage packaging systems. Each equipment page covers applications and configuration; separate sections describe engineering and projects abroad.
What I did
- Name, company and contact details can be filled in automatically by the browser.
- 7 language versions.
- The language is chosen by the visitor’s location.
- The chosen language is remembered for later visits.
Website CMS
- Analytics for an international audience: countries, sources, devices, popular pages and enquiry trends.
- Anonymous views and consented visits are counted separately, so the figures are never mixed without explanation.
- Internal traffic is excluded: visits to the admin panel and previews do not distort statistics for public pages.
- Content, translations and enquiries in one panel: a staff member can maintain the language versions and handle enquiries without switching between systems.
- Different rights for the team: owner, editor and a staff member with view-only access.
- Upload checks for images: format, content, dimensions and allowed file size are verified.
- Login protection and content safety: limited sign-in attempts, managed sessions and a backup export of the content database.
Security
Before handing the project over to the client, an internal grey-box security audit was carried out.
Result: No critical, high or medium vulnerabilities were found in the final build of the project.
Protection against SQL and command injection
- Test: Automated parameter testing with
sqlmapplus manual fuzzing of input forms. - How it is protected: The source code never builds SQL queries by joining strings. The framework’s built-in ORM escaping is used. The application’s database access is limited to
Data Reader/Writerrights, with no access to system tables.
Protection against XSS
- Test: Attempts to inject malicious JS scripts into every user text field.
- How it is protected: A strict template engine with automatic escaping of HTML entities. A strict Content Security Policy (CSP) on the web server blocks any third-party or unsafe inline code.
Component security
- Test: Software composition analysis (SCA) with
SnykandDependency-Check. - How it is protected: All packages are pinned to stable versions with no known vulnerabilities in the NVD database. Automatic notifications are set up for security patches to dependencies.
Admin panel isolation
- How it is protected: The admin panel is moved to a separate subdomain, hidden from search engine crawlers and protected from brute force by
Fail2ban(the IP is blocked after 5 failed attempts). Signing in to the admin panel requires two-factor authentication (2FA / TOTP).
Resilience to DDoS and load
- Test: Stress testing with
k6, simulating a legitimate surge of users and HTTP flood attacks. - How it is protected: Request limits (
limit_req) are set in Nginx and return error 429 when one IP exceeds them. The architecture is ready for seamless integration with external services (for example, Cloudflare / Qrator) to filter L4/L7 traffic.